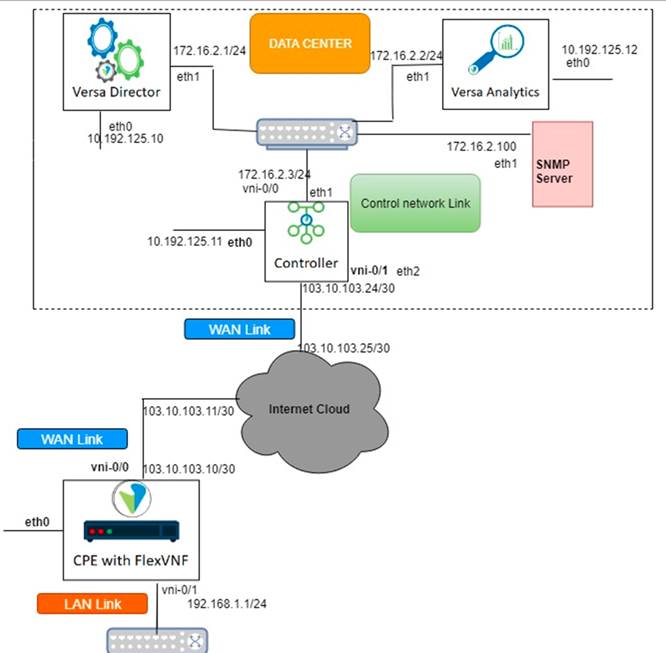
This article describes how to configure SNMP v2c on Versa FlexVNF CPE using Config Templates when the SNMP server is reachable on overlay network.
Prerequisites:
- Versa Headend is installed, configured and running.
- SNMP server is behind the Versa SDWAN Controller (within Data Centre) and is reachable from Versa FlexVNF CPE via the Provider-Control-VR
- In this example SNMP server is reachable on 172.16.2.100 and standard SNMP ports 161 and 162 (trap) are opened on the underlay network.
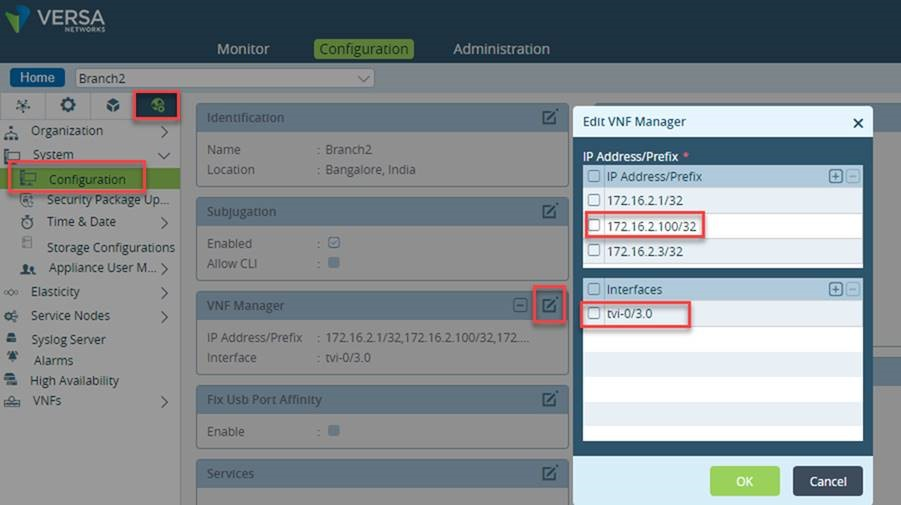
- SNMP Server Address needs to be added in VNF manager and select the interface on which server is reachable, In my reachable via tvi-0/3.0 interface.
NOTE: SNMP polling is not supported over dhcp wan interfaces on VOS and is not configurable from workflow either.
Setup Details
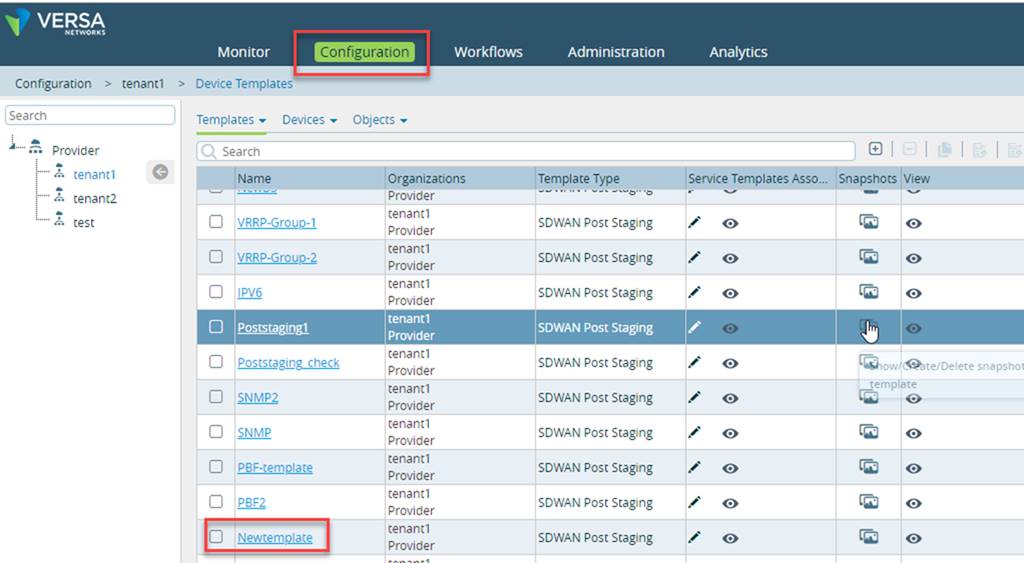
First login into the Versa Director → Navigate to the configuration → Template → Edit the Template associated with the branch
Configuring Communities
Community is a group of devices that SNMP monitors.
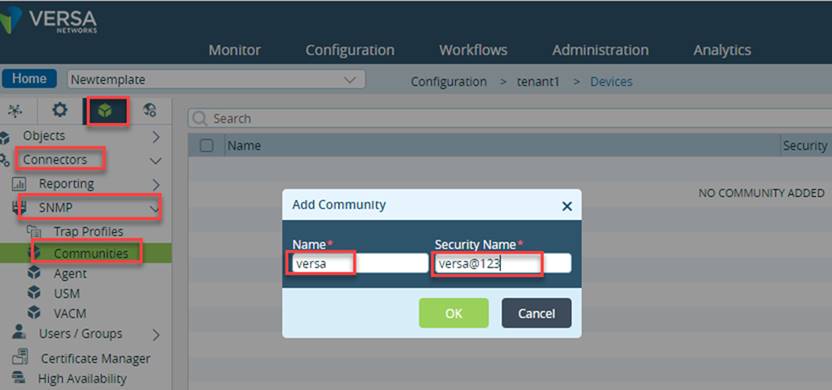
- On the branch template go to the Configuration tab →Objects & Connectors → Connector → SNMP → Click on Communities → Click on (+) symbol to add a new community
NOTE: There is an error in the screenshot below, the community name and security name should always be the "same", and the value should be the community name that you seek to use
For ex, versa123 should be set against community name and security name, if you want to use versa123 as the community name
Field | Description |
Name | Name for the community. |
Security Name | Secure name for the community. |
P.S.: Under Communities, Name and Security Name has to be the same.
- Click OK.
This configures a community.
Configuring SNMP Trap Profiles
SNMP traps are alert messages sent from one or more remote SNMP-enabled devices to a central device, the “SNMP manager.” A trap communicates the health and performance warnings to the SNMP manager. For information on how to configure the profile, refer below steps.
- On the branch template go to the tab → Objects & Connectors → Connector → SNMP → Click on Trap profile → Click on (+) symbol to create new trap profile.
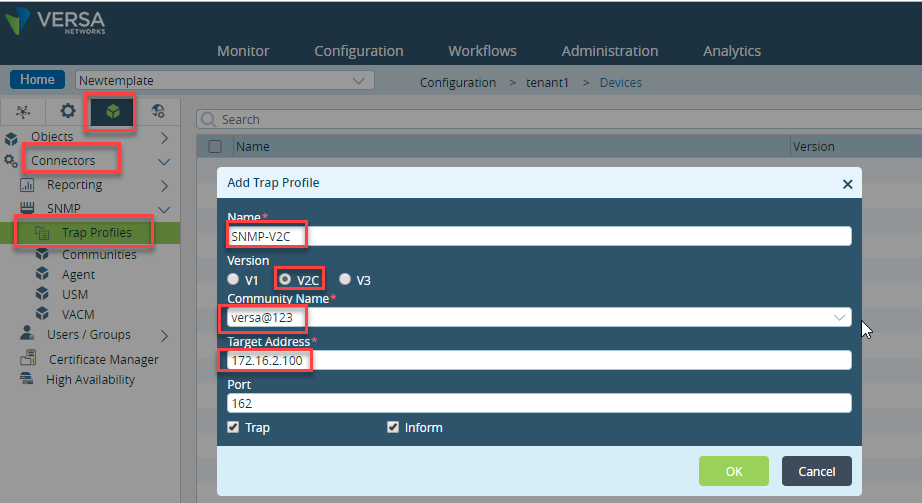
Field | Description |
Name | Name of the trap profile. |
Version | Version of the trap profile: V1 V2C V3 |
Community Name | Community string identifies a community of SNMP managers and monitored devices, and serves as a password to authenticate the community members to each other. |
Target Address | IP address of the SNMP manager. In this case, it is 172.16.2.100 |
Port | Port number assigned to the SNMP manager. |
Trap | Select if SNMP simply sends a message. |
Inform | Select if SNMP sends and gets an acknowledgment for the message sent |
- Click OK once you enter value for required fields.
Configuring SNMP Agent
An agent interacts with SNMP and enables the flow of information between the monitored devices, the applications, and the monitoring device. For information on how to configure the profile, refer below steps to Configuring SNMP agent in the Versa VNF.
- On Branch template go to Objects & Connectors → Connectors → SNMP → Agent → click (+) symbol to edit configure the follow fields
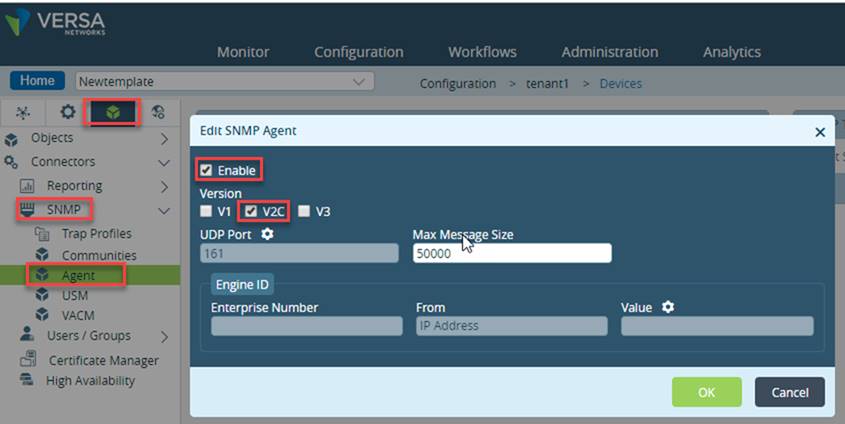
- Then click on edit SNMP target source and enter the IP address of the local tvi interface and click OK
This IP is used as source IP for reaching the SNMP server. As in this case, the SNMP server is reachable using Provider-Control-VR the IP address 10.0.192.103 is that of the tvi interface on the CPE.
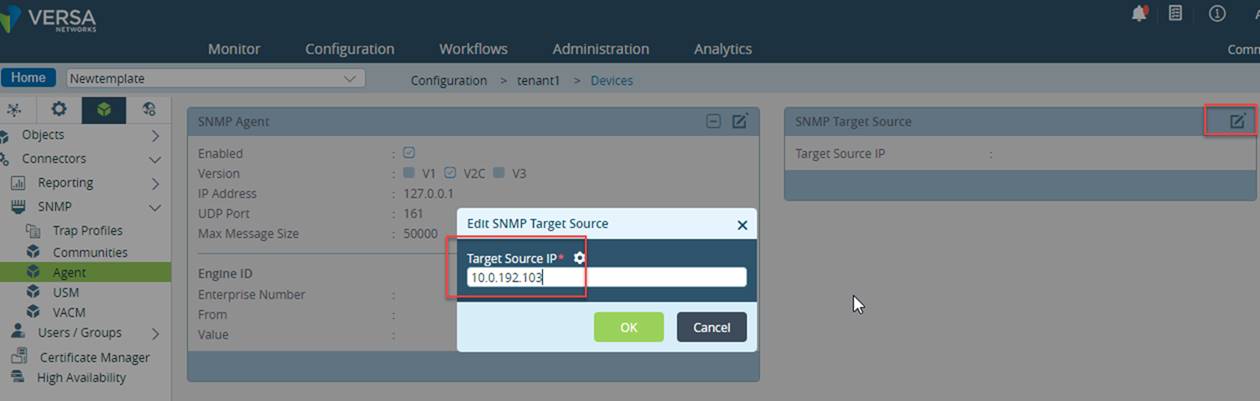
This configures SNMP agent.
Configuring VACM (View-based Access Control Model)
SNMPv2c/v3 uses view-based access control model (VACM), which allows you to configure the access privileges granted to a group. All access control within VACM operates on groups, which are collections of users defined by USM.
The security model is configured for:
- Views
- Groups
Configuring VACM Views
a. In the Director view, go to Configuration > Templates > Device Templates. Select an organization in the left navigation panel and a template from the dashboard.
b. Then navigate to Configuration > Objects & Connectors > Connectors > SNMP > VACM.
c. Click (+) to add a view
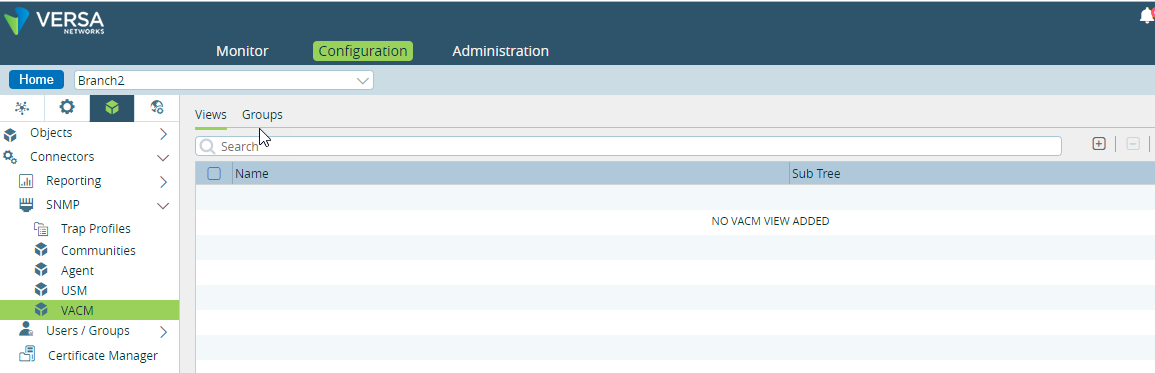
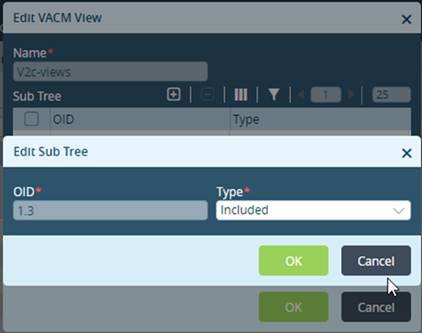
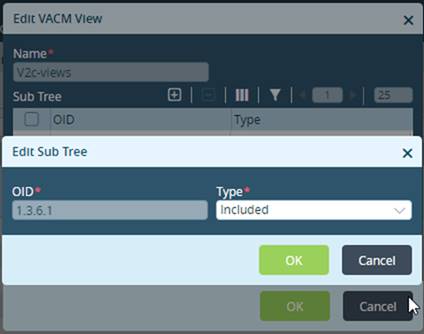
d. Click OK.
This configures a VACM view.
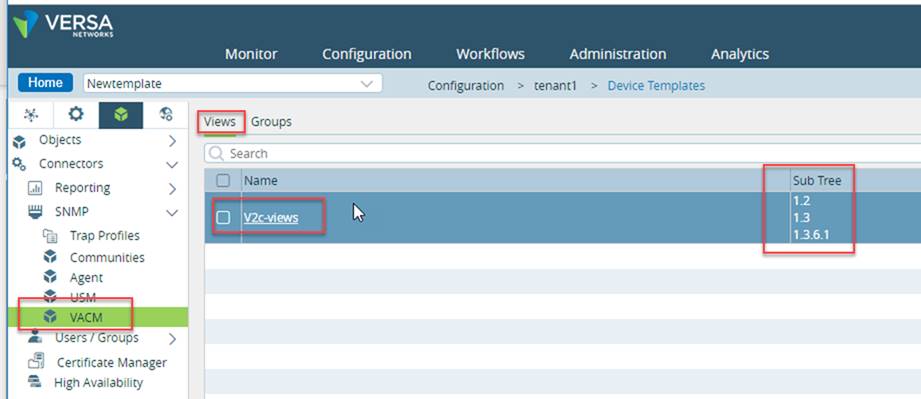
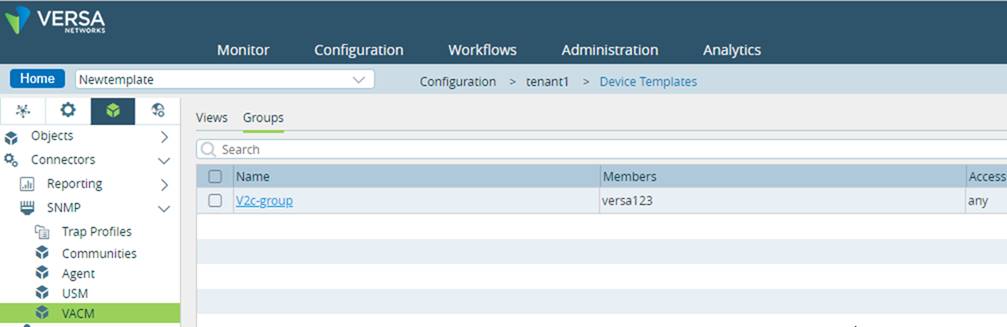
Configuring VACM Groups
- In the Director view, go to Configuration > Templates > Device Templates. Select an organization in the left navigation panel and a template from the dashboard.
- Then navigate to Configuration > Objects & Connectors > Connectors > SNMP > VACM. Click the Group tab.
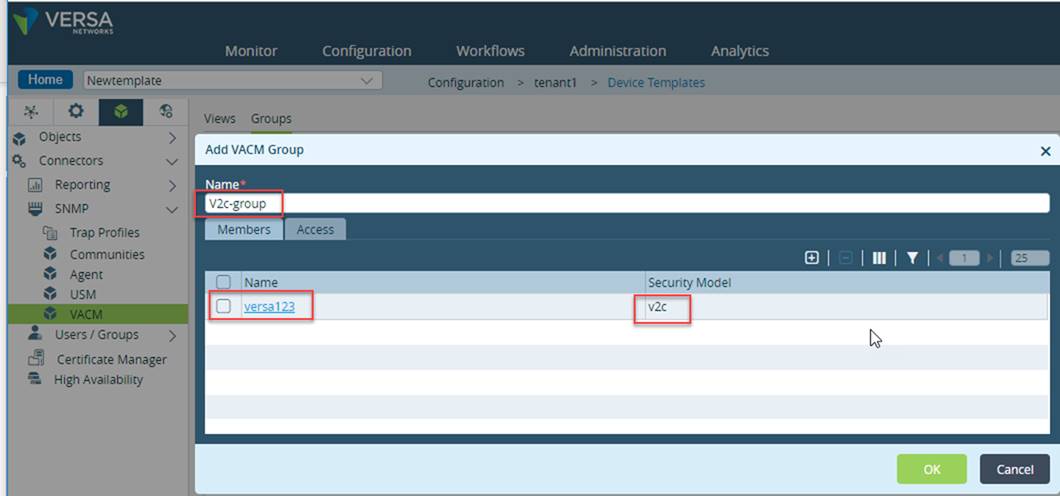
- Click (+) to add a group.
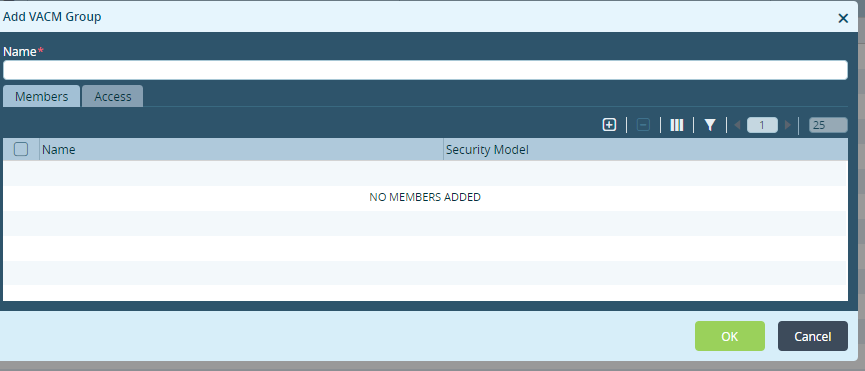
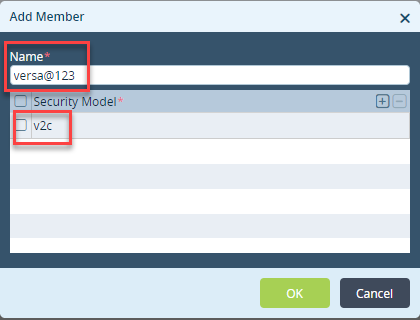
- Click on (+) to add member
- Click (+) to add a security model. NOTE: Make sure the VACM Groups "Members Name" is same as community "Security Name" (sec-name) configure in step 1a.
Field | Description |
Name | Name of the VACM group. |
Field | Description |
Name | Name of the member. |
- Click the access tab
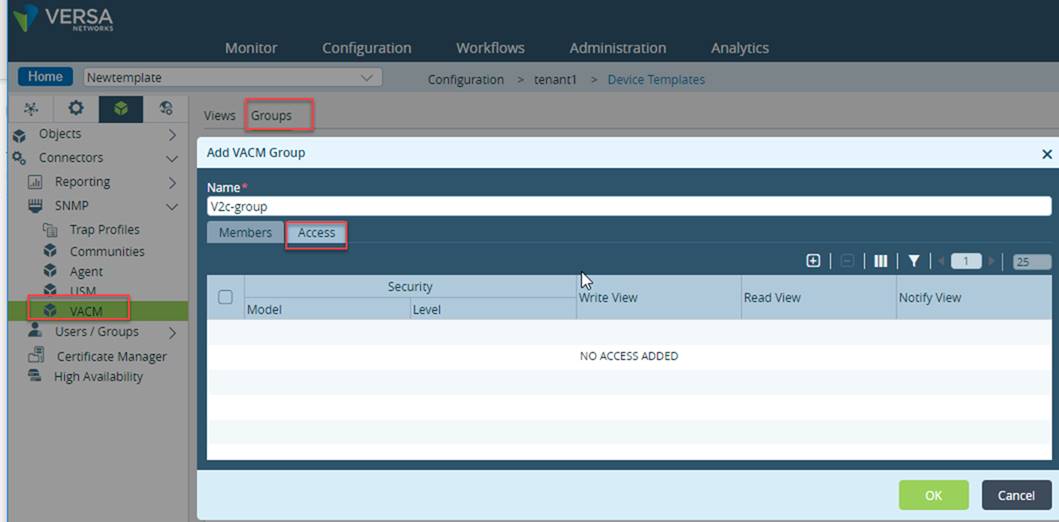
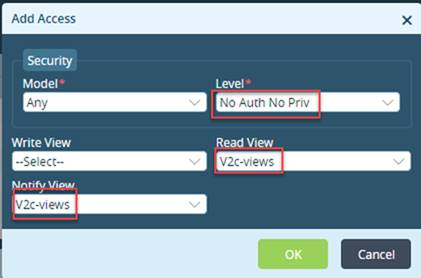
- Click (+) tab to add access
Field | Description |
Security Model | Name of the security model. |
Security Level | Type of security: Auth No Priv Auth Priv No Auth No Priv |
Read View | Object on which to grant read view. |
Notify View | Object on which to grant notify view. |
- Click Ok
- Click Ok
This configures VACM GROUP.
Configure VNF Manager
For SNMP server to be able to poll the FlexVNF and receive the SNMP traps, we need to add SNMP server as VNF Manager settings.
We also need to select Interface using which the Branch will be able to reach the SNMP server. In this case, SNMP server (172.16.2.100 is reachable for Branch from tvi-0/3.0 interface)
Once have done the above steps commit the template to the branch.
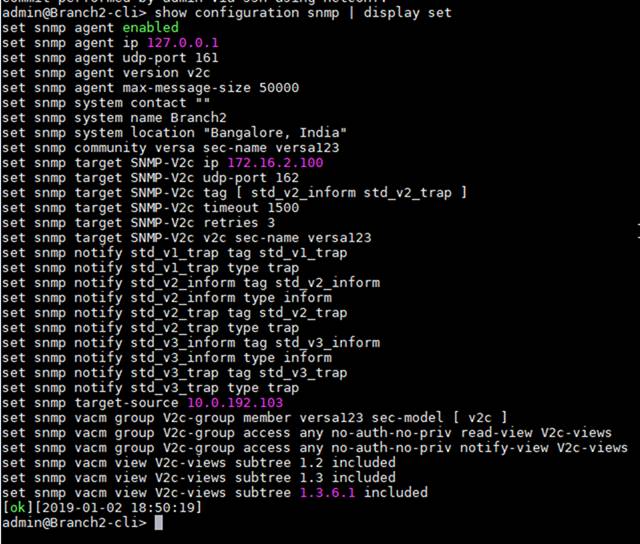
Validate the configuration from FlexVNF CLI
NOTE: There is an error in the screenshot below, the community name and sec-name should be the same
The right configuration would be as below
set snmp community versa123 sec-name versa123