1.NAT function in HA setup with if one internal IP has 2 rules
Setup:
We have 2 devices in HA setup where each device is connected with one ISP link
Consider devices CDO-A and CDO-B, CDO-A is VRRP master and configured WAN interface ISP-1 as primary and CDO-B has VRRP Standby and configured WAN interface ISP-2 as hot-standby.
Hot Standby - Titan only sends direct internet access (DIA) traffic to the interface if the primary interface is down.
Currently as per configuration all the DIA traffic is routed to ISP-1 exit gateway from CDO-A device.
We have configured port forwarding rule on each device CDO-A and CDO-B for an internal IP as 192.168.47.20/32
Requirement : To NAT and route the traffic through device 2 WAN interface ISP-2 (CDO-B)
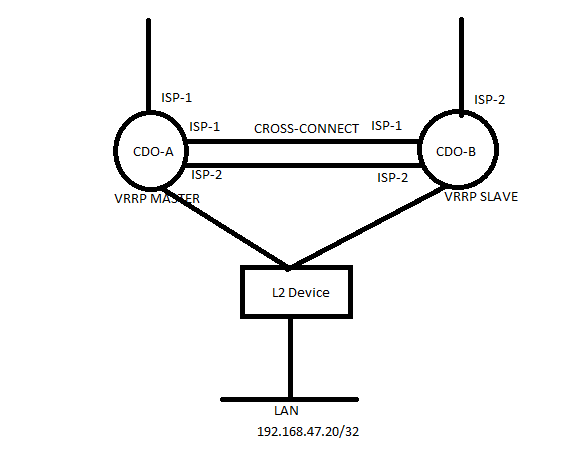
Tested this feature and It can not be round robin, it uses ISP-1, if ISP-1 is down then it uses Secondary ISP-2. As long as ISP-1 up it uses ISP-1 only.
Informed same to the customer about the functionality.
2. Requirement is to divert some specific public traffic via remote branch gateway instead of local breakout.
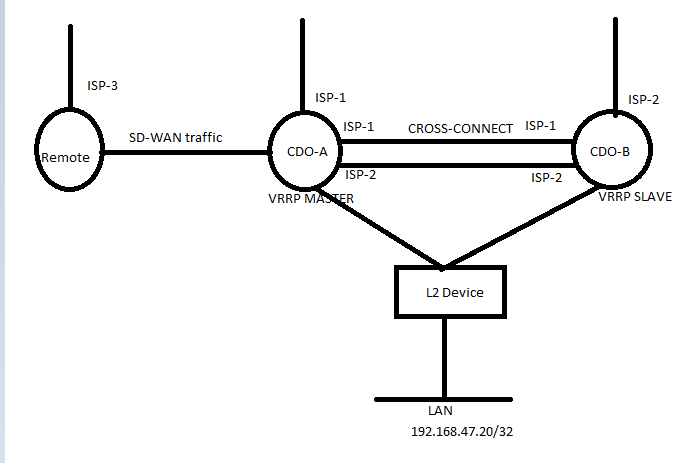
This can be achieved by below steps
If we have LAN based breakout to Internet (option #2).
Customer can do this:
- Lets say the remote branch and Local Branch is CDO-B.
- The Public IP that they want to reach is X
- On A they want to reach X via B instead of local DIA
- On B, On Titan, select LAN -> Ethernet Ports -> Add a Static route to that Public IP X.
- Eg: if X = 182.75.164.17, then add route to 182.75.164.17/32 with Nexthop = LAN's Nexthop through which they will go out to Internet (typically a L3 switch or Firewall).
- This will enable Branch A use B to route to that IP instead of DIA.
If we have Option#1, then after we do # 5 , go to director and for this static route entry select discard and no-install
Further checked with TAC about the requirement
(local branch) ---------- sdwan ----------- (remote branch) ------- ISP
So basically we want to send traffic for a specific dst ip-address (a public ip) towards the remote branch.
We can write a static route in the LAN-vr of the local branch, for this public ip, and point it to the next-hop as the tvi address of the remote-branch, this way all traffic destined to this public ip would be placed over sdwan and it would reach the Lan-vr of the remote-branch.